CraxsRat V7.7 Cracked
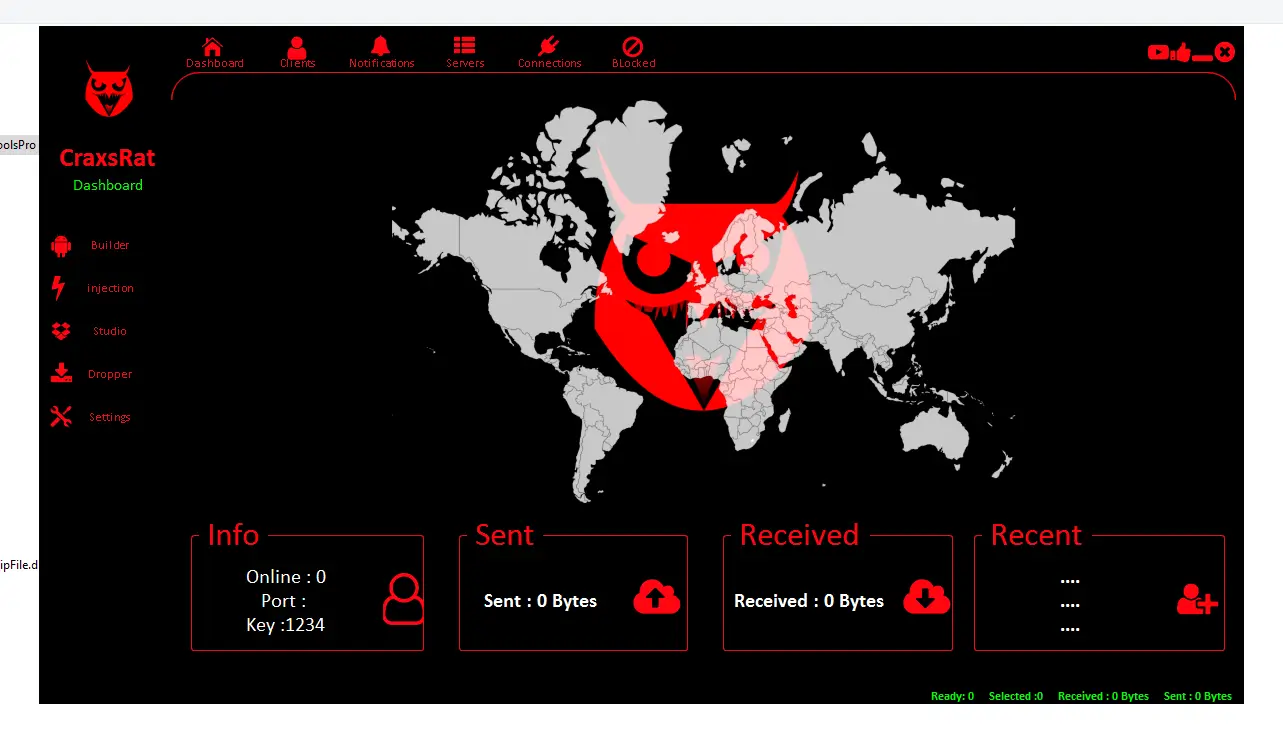
In the ever-evolving cybersecurity landscape, tools like CraxsRat V7.7 Cracked have become a focal point for both ethical researchers and malicious actors. As a sophisticated remote access Trojan (RAT) designed for Android devices, CraxsRat V7.7 Cracked offers extensive control capabilities that can be exploited for penetration testing—or, unfortunately, for scams and fraud. If you're exploring the features, risks, or detection methods of CraxsRat V7.7, this comprehensive guide breaks it down. We'll cover everything from its origins to practical tips for staying safe in 2025.
Whether you're a cybersecurity professional conducting ethical hacking or a user concerned about mobile threats, understanding CraxsRat V7.7 is crucial. Let's dive in.
What is CraxsRat V7.7 Cracked?
CraxsRat V7.7 is the latest iteration of the CraxsRat malware family, a remote access Trojan (RAT) primarily targeting Android operating systems. Evolving from earlier versions like V7.4 and V7.6, this tool grants attackers—or authorized testers—complete remote control over infected devices.
Originating from Spymax RATs, CraxsRat gained notoriety in underground forums and Telegram channels for its adaptability. The V7.7 update, spotted in mid-2025, amplifies its stealth and functionality, making it a go-to for fake app scams and bank fraud campaigns. While marketed as a "remote administration tool" in some circles, its misuse in cybercrime highlights the fine line between legitimate security testing and illegal activities.
CraxsRat V7.7 download sources are often found on dark web repositories or as cracked versions on GitLab threads, but engaging with them poses serious legal and security risks.
Key Features of CraxsRat V7.7 Cracked
What sets CraxsRat V7.7 apart from its predecessors? This version introduces enhanced customization and evasion techniques, allowing builders to tailor payloads for specific attacks. Here's a breakdown of its core capabilities:
1. Remote Control of the Control Device: Full access to compromised Android devices, including browsing, launching apps, and executing commands. Supports dropper modules for stealthy installation, mimicking legitimate app updates.
2. Surveillance and Data Theft: Access to the camera and microphone: live feed for spying without the user's consent. Keylogging and Call Interception: Captures SMS messages, calls, and keystrokes for credential harvesting. File Management: Remotely uploads, downloads, and deletes files.
3. Stealth Operations: Operates silently in the background, evading basic antivirus scans. Screen capture and location tracking for real-time monitoring. Customizable builders (free/paid) allow for variants tailored for banking Trojans or ad fraud.
4. Advanced Evasion Tactics: Integration with Telegram channels for updates and command and control (C2) servers. Support for multilingual tutorials, including Chinese, driving its adoption by global threat actors.
These features of CraxsRat V7.7 make it a powerful tool for ethical penetration testing when used legally, but its proliferation in 2025 has led to a surge in targeted Android attacks.
Feature Description Potential Risk Level Remote Control Full Device Navigation High (Data Exfiltration) Camera/Microphone Live Monitoring Critical (Privacy Invasion) Keylogging Credential Capture High (Financial Fraud) File Management Data Theft/Deletion Medium (Ransomware Tie-in) Stealth Mode Background Operation High (Detection Evasion)
Ethical Uses and Legal Considerations
For white hat hackers, the ethical use of CraxsRat V7.7 Cracked in controlled environments (e.g., bug bounties) can simulate real-world threats. Always obtain written consent and comply with laws such as the CFAA in the United States. Resources such as YouTube tutorials (e.g., on Infinity Hacks) demonstrate safe testing.
Download 1 Download 2 Download 3