Amnesia 0.7.2
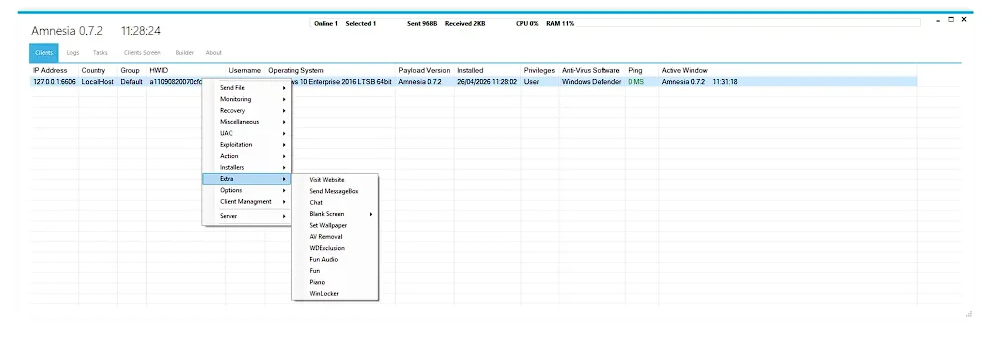
Amnesia 0.7.2 – Complete Windows RAT Malware Analysis
```Amnesia 0.7.2 is a sophisticated Windows Remote Access Trojan (RAT) recognized within cybersecurity research for its modular architecture, command-and-control (C2) infrastructure, persistence mechanisms, and remote administration capabilities. This malware family is designed to maintain communication between compromised systems and remote control servers, allowing operators to manage infected devices through centralized infrastructure. Security analysts frequently study Amnesia RAT to better understand modern cyber threats, malware development trends, Windows security risks, and attacker methodologies used in contemporary threat campaigns.
The architecture of Amnesia 0.7.2 focuses on efficiency, scalability, and operational stability. Its lightweight design enables execution across multiple Windows environments while minimizing resource consumption. Researchers examining this malware often analyze its communication protocols, persistence techniques, system interaction methods, and command execution capabilities to improve threat detection, incident response procedures, and defensive security strategies.
Key Features and Capabilities
- Multi-port command and control server support
- Lightweight and optimized operational framework
- Real-time monitoring and activity tracking functions
- Remote system administration capabilities
- Advanced persistence mechanisms for Windows environments
- System information collection and monitoring features
- Flexible communication infrastructure
- Support for centralized management operations
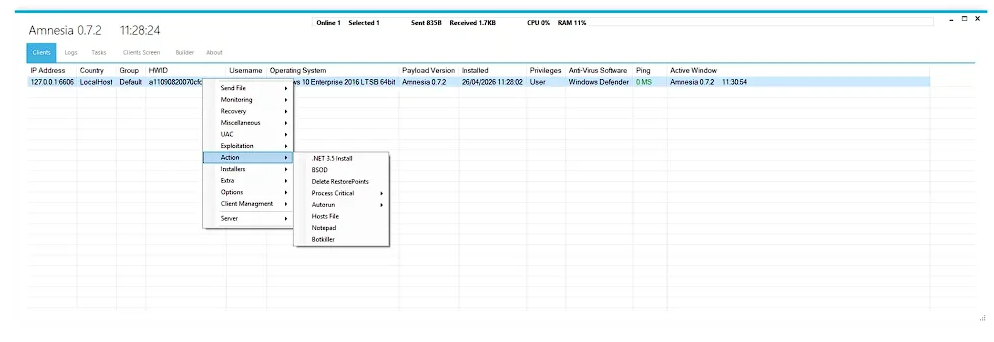
Technical Overview
From a technical perspective, Amnesia 0.7.2 employs a command-and-control architecture that facilitates communication between infected endpoints and remote servers. Such infrastructures are commonly analyzed by malware researchers to identify indicators of compromise (IOCs), network artifacts, persistence techniques, and behavioral patterns associated with Windows-based malware operations. Understanding these mechanisms helps organizations strengthen endpoint security, improve threat hunting activities, and enhance overall cyber resilience.
Cybersecurity Research and Threat Intelligence
Amnesia 0.7.2 remains a subject of interest for malware analysts, SOC teams, digital forensics specialists, incident responders, and threat intelligence professionals. Studying malware families such as Amnesia contributes to a deeper understanding of modern attack chains, persistence methodologies, command-and-control infrastructures, and adversarial tactics. These insights support the development of more effective detection rules, security monitoring processes, forensic investigations, and proactive defense strategies across enterprise Windows environments.
Amnesia 0.7.2, Amnesia RAT, Windows RAT, Remote Access Trojan, Windows Malware Analysis, Cybersecurity Research, Threat Intelligence, Malware Analysis, Digital Forensics, Incident Response, Threat Hunting, Endpoint Security, C2 Infrastructure, Command and Control Servers, Windows Security, Malware Research, Cyber Threat Intelligence, Persistence Techniques, Botnet Analysis, Advanced Malware.
```